Contents
VPN vs Proxy: What's the Difference?
VPNs and proxies both forward your traffic, but they cover different amounts of your device, encrypt differently and work at different layers. A comparison table and sequence diagram explain the difference — and why modern apps combine a virtual adapter with rule-based routing.
How networks work — series: ① What happens when you open a website → ② Network layers → ③ Common network protocols → ④ What is a proxy? → ⑤ What is a VPN? → ⑥ VPN vs proxy → ⑦ What HTTPS encrypts → ⑧ System proxy vs TUN mode → ⑨ Split tunneling → ⑩ DNS poisoning and leaks → ⑪ Why it slows down at night → ⑫ Latency, loss and bandwidth
VPNs and proxies are both middlemen that forward your traffic. They differ in three ways: how much of your device they cover, whether they encrypt, and which layer they work at. A plain proxy usually only handles programs that are configured to use it (like your browser), doesn’t encrypt anything, and works at the application or session layer. A VPN uses a virtual network adapter to capture your whole device, encrypts everything all the way to the server, and typically works at the network layer. Modern apps combine the two: a virtual adapter captures everything, then rules decide what goes through the encrypted tunnel and what connects directly.
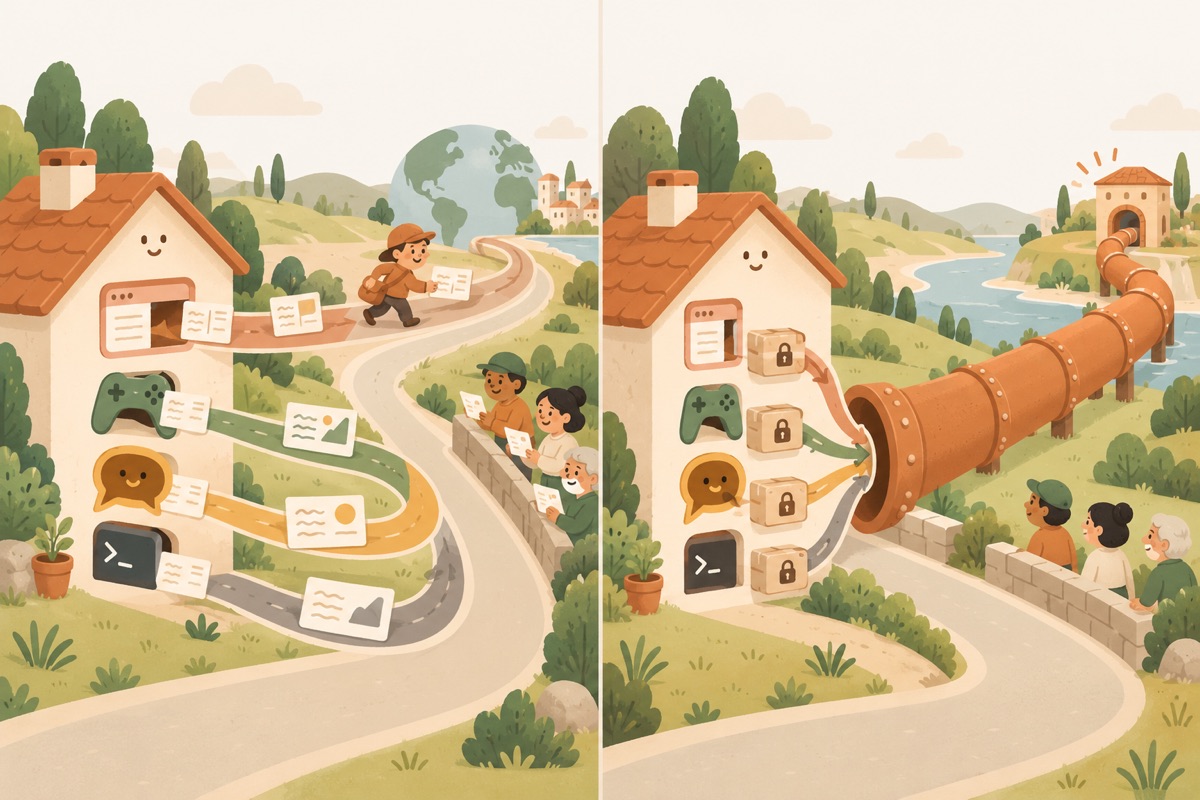
- ① Plain proxyOnly the browser hands its mail to it
- ② Other apps go directGames, chat and the terminal take their own roads
- ③ Visible on the wayContents and destinations can be read
- ④ Whole deviceEvery app's traffic is caught and encrypted
- ⑤ One encrypted pipeEverything flows into one sealed tunnel
- ⑥ VPN serverUnpacks and forwards at the far end
The differences at a glance
| Plain proxy (HTTP / SOCKS5) | VPN | |
|---|---|---|
| Layer | Application / session: forwards individual connections or requests | Usually network: forwards whole IP packets |
| Coverage | Only programs configured to use it — and that honour the setting | Every program on the device, including command-line tools and games |
| Encryption | None of its own | Encrypted all the way from device to server |
| What onlookers see | Which addresses you reach through the proxy, plus anything unencrypted | Only that you’re connected to the VPN server |
| System permission | Usually none | Required — creating a virtual adapter needs your approval |
| Typical uses | Office gateways, routing just the browser, development and debugging | Public Wi-Fi protection, remote work, whole-device access to other regions |
Difference 1: coverage — one program or the whole device
A proxy relies on programs cooperating: your browser reads the system’s or its own proxy settings and hands requests to the proxy. Plenty of programs never read those settings — command-line tools, some games, some chat apps — and simply connect directly.
A VPN takes a different route. It creates a virtual network adapter and points the default route at it. Programs don’t need any settings: every packet they send passes through the virtual adapter and lands in the tunnel. See What is a VPN? and System proxy vs TUN mode for how that works.
Difference 2: encryption — can contents and destinations be seen?
The HTTP proxy and SOCKS5 protocols don’t encrypt anything. On the hop to the proxy, anyone on the same Wi-Fi or your ISP can see which address you’re asking the proxy to reach, can read plain-HTTP pages in full, and can even read your proxy username and password.
A VPN builds an encrypted channel between your device and the VPN server. Onlookers only see that this device is talking to the VPN server, plus the size and timing of the data.
Side by side in one sequence diagram
Say your computer is running a browser and a game at the same time. Here’s how traffic flows with a plain proxy (set only in the browser) versus a VPN:
| Step | What happens | What your ISP sees |
|---|---|---|
| ① | The browser hands its request to the proxy, with the destination spelled out | That you use a proxy, and where you’re going |
| ② | The proxy visits the site for you | — (this leg is between the proxy and the site) |
| ③ | The game ignores the browser’s proxy setting and connects directly | Every one of the game’s connections, as if there were no proxy |
| ④ | Browser traffic enters the virtual adapter, is encrypted and sent to the VPN server | Encrypted data only — no destination |
| ⑤ | The game’s traffic is caught by the virtual adapter and encrypted too | Encrypted data only — no destination |
| ⑥–⑦ | The VPN server decrypts it and visits the site or game server for you | — (this leg is between the server and the site) |
Difference 3: the layer they work at
- HTTP proxies work at the application layer and understand HTTP, so they see the URL you request (just the domain with HTTPS);
- SOCKS5 works at the session layer and just relays TCP / UDP connections, without caring what protocol runs inside;
- VPNs typically work at the network layer, encrypting and wrapping whole IP packets, so any protocol on top gets carried.
For a refresher on layers, see The OSI model and TCP/IP layers.
What modern apps do: a virtual adapter plus routing rules
These days the line between the two is blurry. Most modern clients work like this:
- A virtual adapter (TUN) captures all of the device’s traffic, with no need for programs to cooperate;
- Rules split the traffic: local sites and LAN devices go direct, overseas services go through the encrypted tunnel, and ad domains can be blocked outright;
- An encrypted protocol carries the tunnelled traffic, so nobody along the way can see its contents or real destination.
You get a VPN’s whole-device, fully encrypted coverage without sending everything the long way round — local sites stay fast. That’s how Pangolin works; see Custom routing rules for the routing settings.
Which should you use?
| What you need | Better fit |
|---|---|
| Change the browser’s exit point for a quick task | A proxy is fine |
| Use the gateway your office or school network requires | A proxy, as your network admin specifies |
| Stay private on airport or café Wi-Fi | A VPN |
| Reach overseas services from command-line tools, games and every app | A VPN (virtual adapter) |
| Keep local sites fast while overseas services stay reliable | Virtual adapter + routing rules |
Related reading
FAQ
Is a VPN always slower than a proxy?
No. Encryption costs very little on modern devices; speed mostly comes down to the route and how far away the server is. A good VPN route is often much faster than a crowded free proxy.
Isn't a proxy plus HTTPS just as safe as a VPN?
Not quite. HTTPS protects page content, but if the hop to your proxy isn't encrypted, anyone along the way can still see which sites you reach through it — and only programs configured to use the proxy are covered.
Why do some apps call themselves a proxy but still cover the whole device?
Modern clients typically capture all traffic with a virtual adapter on your device, then send it to the server over an encrypted proxy protocol. By how they capture traffic they're VPNs; by the protocol they speak they're proxies. The line has blurred.
Don't have Pangolin yet?
Available for iPhone / iPad, Mac, Windows and Android. New accounts get a free 7-day Pro trial.
Download the app